Organizations are increasingly adopting cloud solutions, with a clear shift toward multi-cloud deployment models. According to the Flexera 2025 State of the Cloud Report, over 70% of companies are using a mix of public and private cloud environments, typically involving two to four public cloud providers. This increased flexibility raises the stakes for cloud security, which has become a major concern for companies and their data centers.
This situation exposes companies to multiple risks. Fragmented tools, inconsistent security policies, lack of centralized visibility and expanding attack surfaces are common threats. Not surprisingly, 77% of companies rank security among their top cloud concerns, just after cost management.
Cloud environments have also become prime targets for cyberattacks. Configuration errors, poorly secured interfaces and even cloud services are exploited as attack infrastructures. Human error remains the leading cause of breaches, accounting for 31% of incidents, a rate that surpasses technical vulnerabilities.
Maintaining data resilience and sovereignty depends on more than just the multi-cloud strategy adopted. Drawing on our consulting experience, we’ve identified the most common cloud security pitfalls to avoid.
Cyberattacks: a direct consequence of inadequate security practices
When it comes to cloud security, a number of recurring mistakes open the door to cyberattacks.
For each mistake, we’ll go over:
- The consequences: What actually happens inside the system.
- The strategic impact: What it means for the organization and its management.
- The solution: Best practices to prevent the vulnerability.
- Key questions: Questions managers can ask their teams to assess if their security measures are effective.
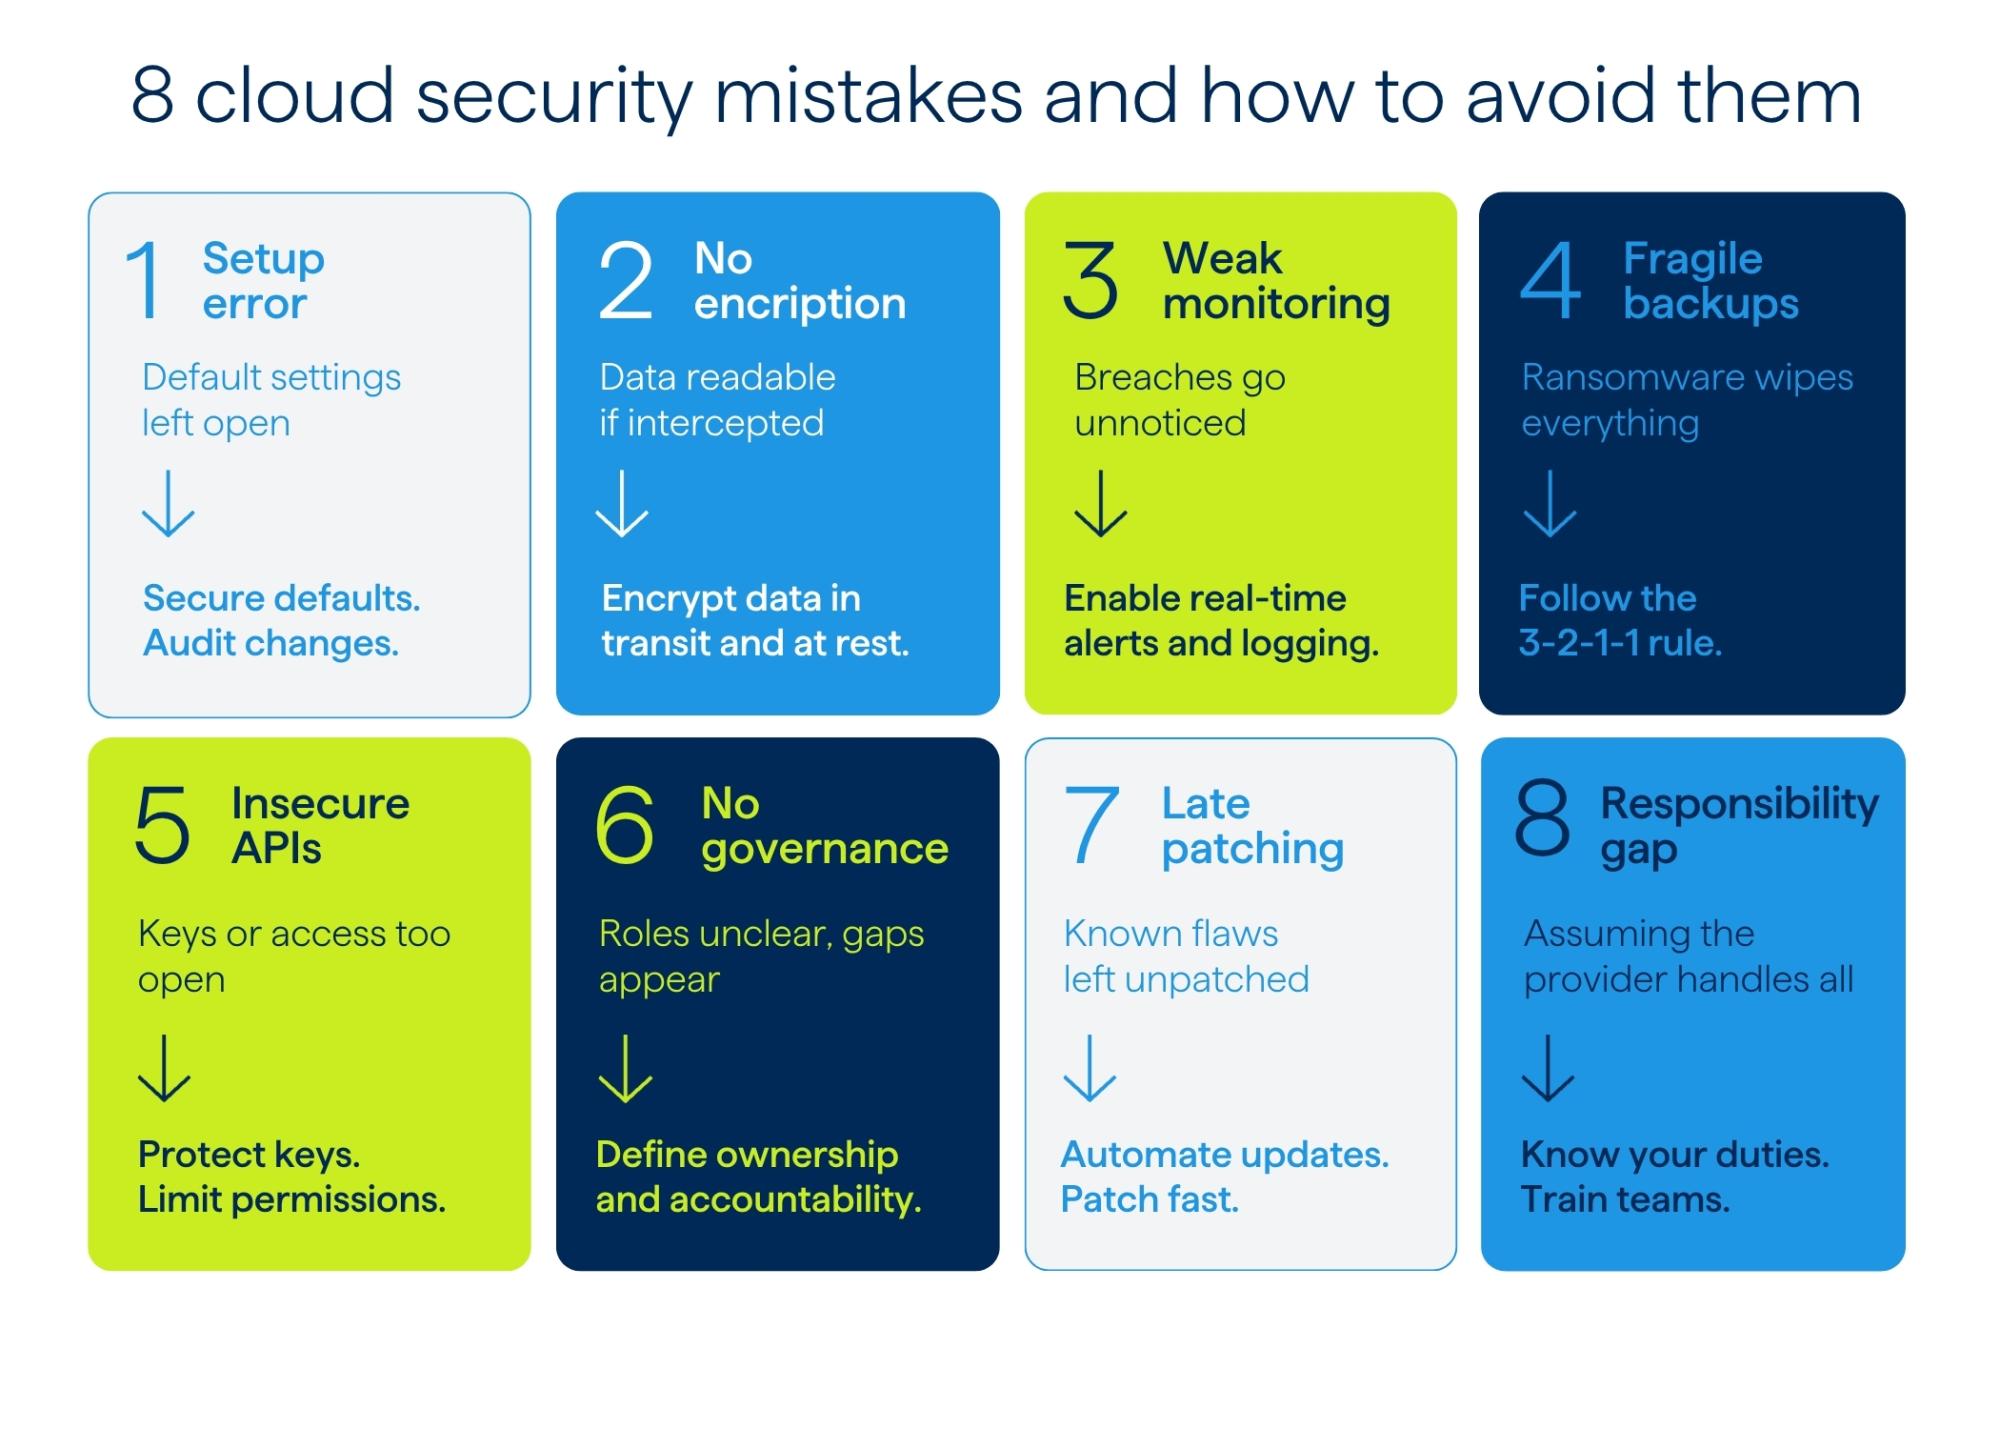
1. Misconfiguration of the cloud environment
This is the most common vulnerability, and also the most costly. It occurs when a cloud environment or a system deployed within it (such as storage, a database or a service) is not properly configured. This often results from default settings or unsupervised technical changes. Attackers exploit these flaws to break into cloud services and compromise an organization’s IT resources.
According to a Gartner survey, 80% of cloud security incidents stem from misconfiguration-related issues. In 2024, Football Australia suffered a major data breach impacting both internal systems and personal data. The incident was caused by poorly configured cloud storage, insufficient oversight of technical changes and an overreliance on cloud service providers.
Mistake:
- Deploying services with unsecured default settings
- Not segmenting or isolating resources
- Failing to properly log or monitor changes
Consequences:
- Unauthorized access to critical systems
- Unintentional exposure of sensitive data
Strategic impact:
- Massive breach of sensitive data
Solution:
- Implement secure configuration templates from the start of deployment
- Use security posture analysis tools to detect errors
- Implement automated controls to monitor changes
- Conduct regular audits of the cloud environment
Key questions:
- Which cloud services are currently exposed to the internet?
- When was the last configuration audit carried out?
- Is there a mechanism in place to detect unauthorized changes?
- Are critical environments properly segmented and encrypted?
2. Not encrypting data
Failing to encrypt data can quickly lead to a serious crisis. If an attacker gains access to the data, they can use it immediately with no technical obstacles. Whether stored in the cloud or moving between services, unencrypted data poses a major security risk. Without encryption, sensitive data is immediately exposed if it’s intercepted.
According to the IBM Cost of a Data Breach Report 2024, robust encryption can reduce the average cost of a data breach by almost half. However, many organizations continue to rely solely on their cloud provider’s default settings, without activating advanced encryption options.
Mistake:
- Storing unencrypted sensitive data
- Transmitting information without adequate encryption
- Relying too heavily on the cloud provider’s default settings
Consequences:
- Intercepted data becomes instantly readable
- Higher risk of compromise from unauthorized access
Strategic impact:
- Regulatory penalties for non-compliance (GDPR, HIPAA, etc.)
- Loss of contracts or certifications with rigorous standards (ISO 27001, SOC 2, etc.)
- Exposure of intellectual property
Solution:
- Always enable encryption for data at rest and in transit
- Keep encryption keys secure and separate from data
- Regularly check compliance with security and data protection standards (GDPR, ISO, etc.)
Key questions:
- Is our sensitive data encrypted both at rest and in transit?
- Where are our encryption keys stored, and who can access them?
- Are we in compliance with relevant data protection standards (GDPR, ISO, HIPAA, etc.)?
3. Inadequate monitoring and oversight
Many organizations deploy their cloud environment without putting a strong monitoring system in place. Activity logs are often incomplete, poorly configured or deleted too quickly. This lack of visibility prevents their security teams from promptly detecting incidents, giving attackers a valuable window to act undetected.
Occasional monitoring is no longer sufficient. Continuous monitoring has become crucial in today’s dynamic cloud environments. Yet many companies still rely on sporadic checks conducted only a few times per year. According to the Verizon Data Breach Investigations Report 2024, nearly 70% of security incidents are detected by third parties like clients, partners or media, revealing major gaps in internal detection capabilities.
Mistake:
- Setting up cloud environments without properly configuring logging and monitoring
- Limited retention or fragmentation of activity logs
- Absence of real-time alert mechanisms
Consequences:
- Breaches remain undetected for days or even weeks
- Attacks discovered by third parties like clients, partners or media
- Delayed responses to incidents, aggravating their impact
Strategic impact:
- Prolonged operational downtime and significant financial losses
- Greater risk of regulatory non-compliance
Solution:
- Ensure activity and access are fully logged across all cloud environments
- Consolidate logs into a centralized security information and event management (SIEM) platform
- Set up automated alerts to detect abnormal behavior in real time
- Conduct regular audits of monitoring and oversight processes
Key questions:
- What activity logs do we retain, and for how long?
- How many incidents have we detected internally versus those reported by third parties?
- Do we have a real-time alert system in place for suspicious or abnormal behavior?
- Are our logs centralized, correlated and analyzed effectively?
4. Inadequate or poorly secured backups
With ransomware on the rise, maintaining reliable and well-protected backups has become a strategic necessity. However, many organizations incorrectly assume that the cloud automatically ensures data availability and security. As a result, backups are often absent, misconfigured or stored in the same environment as the original data, leaving them exposed to the same threats.
In the event of an attack, accidental deletion or technical failure, the absence of secure copies can lead to the permanent loss of critical information. Without a proven recovery plan, restoring operations becomes slow, costly and sometimes even impossible.
Mistake:
- Assuming the cloud provider automatically ensures data protection and availability
- Storing backups in the same environment as the original data
- Not routinely testing recovery plans
Consequences:
- Data cannot be recovered after a ransomware attack or system failure
- Backups are compromised or unusable
- Recovery takes longer and costs escalate
Strategic impact:
- Operations halt, resulting in significant financial losses
- Long-term disruption to business continuity
Solution:
- Establish a regular, automated and verified backup policy
- Periodically test recovery plans to ensure they are effective in real-world conditions
- Document and audit backup and recovery processes
- Retain at least one copy of the backups offline or in an environment isolated from the original cloud environment
Tip:
To ensure data availability and security in the event of an incident, apply the 3-2-1-1 rule:
- Keep 3 copies of the data
- On 2 different media types (for example, cloud and local disk)
- Retain 1 copy offsite, preferably isolated from the main cloud environment
- Maintain 1 immutable or offline copy, protected from changes and attacks
This approach significantly reduces the risks associated with ransomware and technical failures. It ensures a fast and reliable recovery even in the event of a major compromise.
Key questions:
- Where are our backups stored, and are they isolated from the rest of the cloud environment?
- How often do we test our data recovery processes?
- What would happen if we were hit by a ransomware attack tomorrow morning?
- Do we have a copy stored offline or in a separate environment?
5. Poor management of APIs and third-party services
Modern cloud environments depend on extensive integration with external services, including SaaS applications, automation tools and business platforms. Most of these connections run through application programming interfaces (APIs), serving as gateways into your systems.
When not properly secured, these APIs present prime entry points for attackers. All too often, access keys are left in plain text, permissions are overly broad and authentication mechanisms are insufficient. A single flaw in an API can put the entire system at risk.
Mistake:
- Storing your organization’s access keys in code or public repositories
- Granting third party services overly broad permissions
- Failing to implement strong authentication for sensitive APIs
Consequences:
- Access keys are exposed or compromised
- Breaches through poorly secured third party services
- Attacks spread rapidly across all connected systems
Strategic impact:
- Sensitive data and critical systems are compromised
- Damage to business relationships
- Significant legal risks
Solution:
- Maintain a complete and up-to-date inventory of active APIs and integrations
- Apply the principle of least privilege to restrict access
- Protect API keys (never store them in plain text) and use infrastructure that safeguards the organization’s cryptographic keys
- Set up strong authentication (OAuth, secure credentials, etc.)
- Implement routine checks and security testing for APIs
Key questions:
- Do we have an inventory of all active APIs and integrations?
- Where and how do we store our API keys?
- What permission limits do we apply to third party services?
- Are our critical APIs protected through strong authentication and granular access control?
6. Lack of clear governance and defined responsibilities
As cloud environments become more complex, securing them requires tackling not only technical aspects but organizational ones as well. This raises important questions that need to be addressed head-on. Who is responsible for monitoring access, reviewing configurations and ensuring proper data segmentation? Without clear governance, grey areas emerge, raising the risk of long-term security issues.
While asking these questions is a part of best practices for cloud asset management, the reality on the ground often falls short. In fact, a 2024 PwC study revealed that over 60% of organizations report a lack of clarity in assigning responsibilities for cloud cybersecurity.
Mistake:
- Migrating to the cloud without clearly defining roles and responsibilities regarding security, including for internal teams, providers and partners
Consequences:
- Lack of clarity in security management
- Vulnerabilities left unchecked due to unclear responsibilities
- Unrealistic expectations of providers or partners
Strategic impact:
- Failed security or compliance audits
- Regulatory penalties and costly legal disputes
Solution:
- Establish clear cloud security guidelines embedded within the organization’s overall policies
- Create a structured governance framework (for example, using the RACI model) to clarify roles, responsibilities and processes
- Provide ongoing training for teams on the specific responsibilities associated with each provider and each type of cloud service
Key questions:
- Who is responsible for the security of our cloud data: us, the provider or a partner?
- Do we have clear and well-defined management policies that are approved by the organization’s leadership?
- Do we have a governance framework, embedded in existing policies (such as RACI), that allows us to clearly define roles and responsibilities?
- Which poorly defined responsibilities could negatively impact the organization’s security posture?
7. Applying updates and patches too late
Cybercriminals don’t always need to innovate. They often exploit known vulnerabilities left unaddressed due to negligence or lack of diligence. The Log4j2 incident in December 2021 is a striking example. A critical vulnerability in the Log4j2 Java library allowed attackers to execute code remotely without authentication. While patches were quickly released, many organizations were slow to implement them, leaving their systems exposed to attacks for several months.
In cloud environments, this problem is amplified by the complexity of the infrastructure and the speed of deployments. Virtual machines, containers and SaaS applications all need to be regularly updated to remain secure.
Mistake:
- Not systematically applying available patches to virtual machines, containers or applications
- Failing to apply updates to third party and open-source components
- Not having automated processes in place to manage vulnerabilities
Consequences:
- Known vulnerabilities can be exploited for weeks or even months
- Vulnerable systems are exposed to targeted attacks
- Stakeholders view slow responses as avoidable
Strategic impact:
- Highly publicized attacks are perceived as preventable, which can harm the organization’s reputation
- High costs associated with crisis management, remediation and operational losses
Solution:
- Automate patch management across all cloud environments
- Implement regular vulnerability scans to detect obsolete components
- Ensure critical patches are applied immediately upon release
- Document and audit update timelines to ensure compliance
Key questions:
- On average, how quickly do we apply critical patches after they are released?
- Who is responsible for monitoring vulnerabilities in our cloud environments?
- Have we automated patch management?
- Are our update processes regularly audited and monitored?
8. Not understanding the shared responsibility model
Too often, organizations assume that “the cloud provider takes care of everything.” In reality, according to the shared responsibility model, security is jointly handled by both parties. The provider secures the infrastructure (hardware, network, hypervisor), while the client organization is responsible for the security of data, identities, configurations and access.
Overlooking this distinction leads to exposed areas, unrealistic expectations of the provider and gaps in the overall security posture.
Mistake:
- Believing that the cloud provider handles all aspects of security, including data, access and configurations.
Consequences:
- Critical areas left without adequate protection
- Unrealistic expectations of the provider
- Misalignment between actual and perceived responsibilities
Strategic impact:
- Company bears legal liability for incidents
- Costly legal disputes could disrupt operations
Solution:
- Train teams on how the shared responsibility model applies to each provider (AWS, Azure, Google Cloud, etc.)
- Clearly incorporate responsibilities into internal security and governance policies
- Conduct regular audits to ensure responsibilities are properly upheld by both parties
Key questions:
- Do our teams clearly understand the provider’s responsibilities versus our own?
- Do we have an internal policy aligned with the shared responsibility model?
- When was the last time we trained our teams on this model?
- If an incident occurs, do we clearly know who is responsible for what?
Cloud security: Staying vigilant is a strategic priority
The cloud is a powerful driver of innovation, but ensuring its security requires constant diligence from organizations. As recent events illustrate, the greatest damage isn’t always caused by the most sophisticated attacks. Many of these incidents result from predictable vulnerabilities that greater vigilance could have prevented.
An organization’s reputation is one of its most valuable assets. Securing your cloud environments keeps your data safe while preserving the trust placed in your organization. Security isn’t a standalone project; it needs to be integrated into governance, everyday operations and organizational culture.
Ultimately, an effective and secure multi-cloud strategy must be capable of:
- Rapidly resolving vulnerabilities
- Preventing errors
- Fostering a culture of continuous vigilance
Take action to secure your cloud environments
Bolstering the security of your environments starts with identifying and fixing the most common mistakes. Our cybersecurity consultants help organizations operating in multi-cloud environments to:
- Assess and prioritize their risks
- Strengthen governance and compliance
- Build lasting operational resilience
If you want to review your current approach or determine where to start, our team can guide you through practical next steps to protect your data and reinforce trust. Get in touch with our cybersecurity experts today.
This article was written in collaboration with: Xavier Desjardins-Rousseau